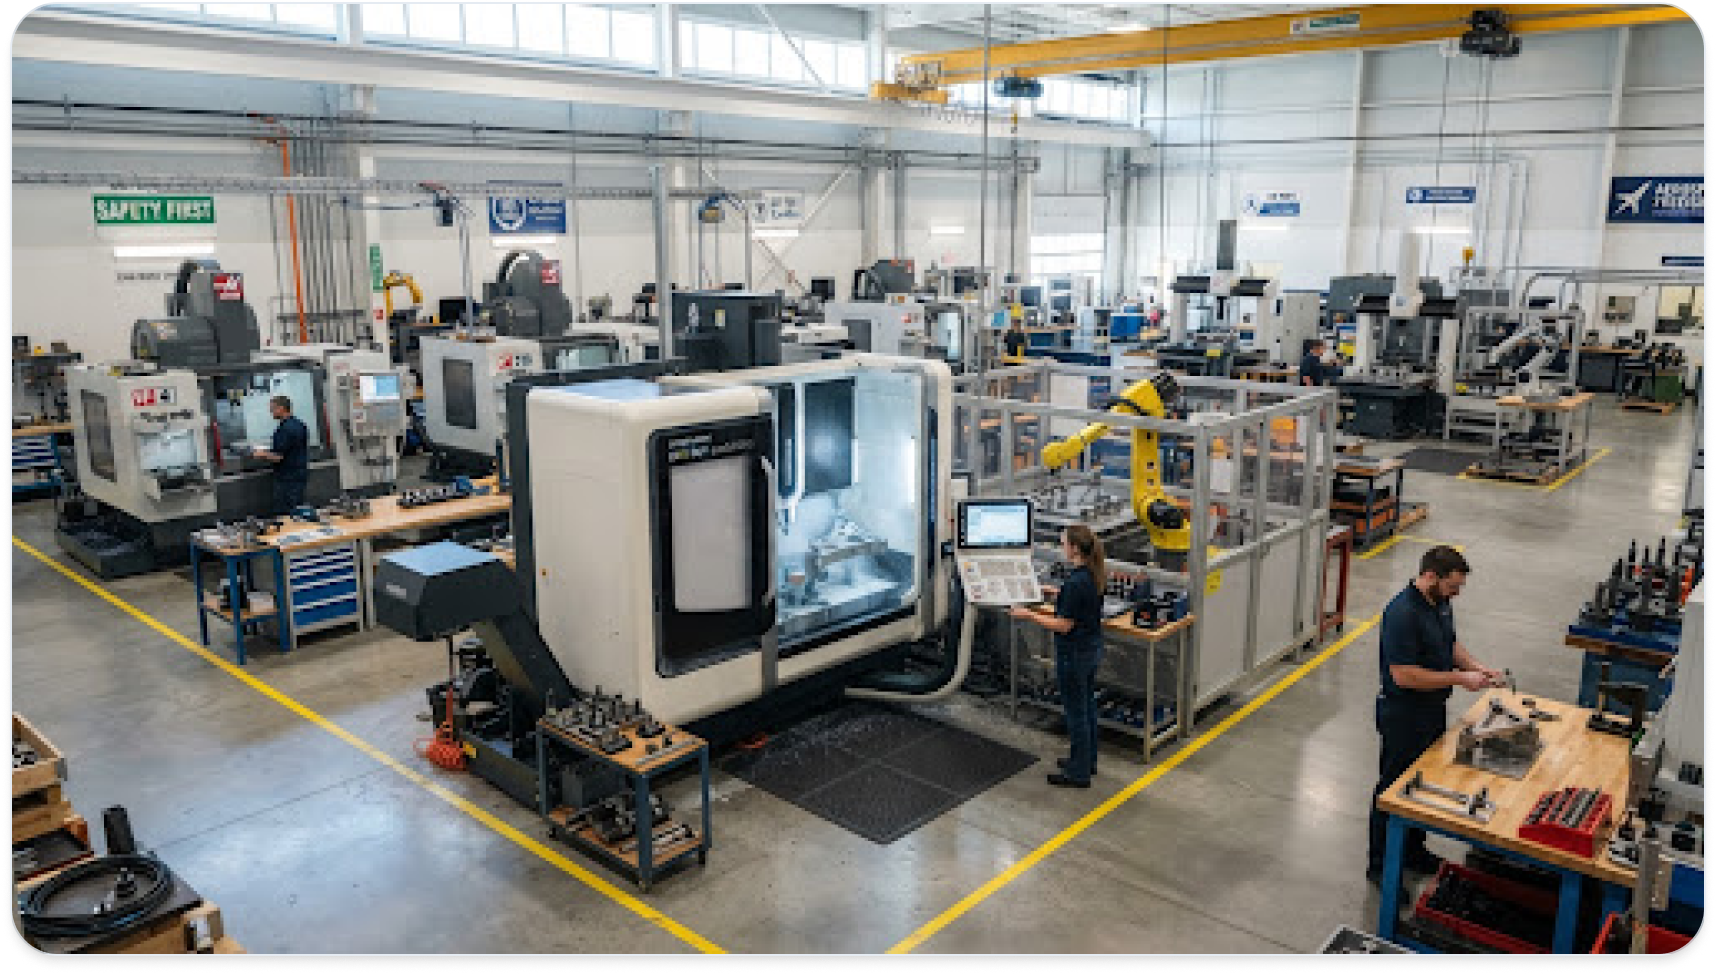
Over the past eighteen months, small aerospace and defense machining operations have faced an unprecedented shift. Where prime contractors once accepted self-attestation checkboxes on simple vendor surveys, they are now deploying technical assessment teams, requiring multi-tenant enclave proofs, and demanding strict boundary evidence before purchase order authorizations are finalized.
For companies with 15 to 75 shop-floor staff, this shift can feel overwhelming. Many owners assume that cybersecurity means spending hundreds of thousands of dollars on enterprise software solutions designed for Fortune 500 enterprises. In reality, modern compliance frameworks prioritize demonstrable segregation, rigorous access hygiene, and disciplined asset tracking.
Why Cybersecurity Matters for Small Manufacturers
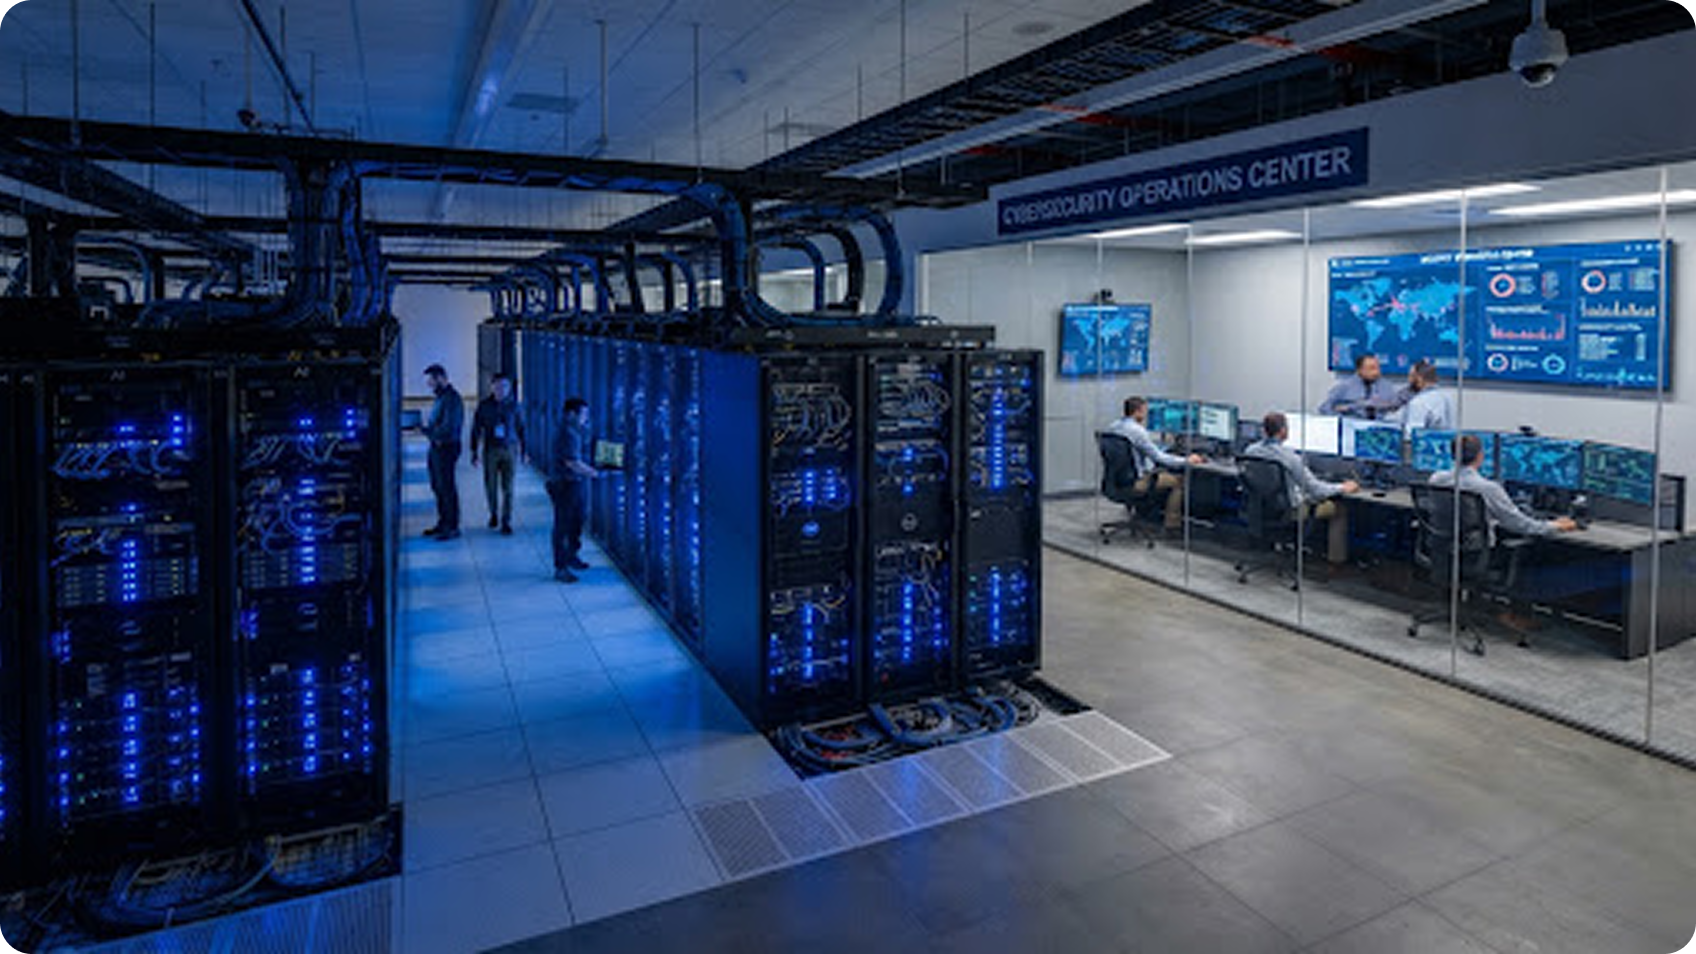
Machine shops are rarely targeted by sophisticated nation-state actors for espionage directly against the shop itself. Rather, adversaries look for the path of least resistance into defense supply chains. Computer-Aided Manufacturing (CAM) workstations, CAD files containing Controlled Unclassified Information (CUI), and direct network-attached CNC mills have become primary targets for credential exfiltration and ransomware disruptions.
Customer Requirements Are Changing
The commercial pressure is no longer hypothetical. Tier 1 aerospace integrators and government agencies have formalized validation checks into standard contract terms:
- Technical verification before release: Prime contractors now require verifiable SPRS scores and System Security Plans (SSPs) before releasing contract drawings.
- Cascading obligations down to machine shops: Small sub-tier contractors with 10–50 personnel are held to the exact standard as prime defense contractors.
- Insurability prerequisites: Commercial cyber carriers are actively denying policy renewals without enforced multi-factor authentication (MFA) across all endpoints.
Start With What You Already Have
Most small operations do not need a wholesale replacement of IT hardware. By establishing clear network boundaries and separating administrative accounting computers from production machine controls, facilities can substantially reduce their compliance footprint.
The key is practical, stepped implementation. Taking an objective inventory of physical assets and digital dependencies enables manufacturers to answer prime contractor surveys with documented confidence rather than guesswork.
What Small Manufacturers Should Know About Cybersecurity
A practical look at the security controls manufacturers should consider as their customers increasingly expect [...]
Read articleOct
Common Security Gaps in Small Businesses
A practical look at several areas where smaller organizations often have room to improve.
Read articleOct
Security Documentation: More Than Just Paperwork
Why documenting security practices matters when customers, auditors, or contracts require evidence.
Read articleOct
Why IT Security Starts With Knowing What You Have
Before improving security, organizations need a clear picture of their systems, users, devices, and information.
Read articleOct
Understanding NIST 800-171 Without the Jargon
A plain-language introduction to the framework and what it means for businesses handling controlled unclassified [...]
Read articleOct
What Small Manufacturers Should Know About Cybersecurity
A practical look at the security controls manufacturers should consider as their customers increasingly expect [...]
Read articleOct
What Small Manufacturers Should Know About Cybersecurity
A practical look at the security controls manufacturers should consider as their customers increasingly expect [...]
Read articleOct

Hi, this is a comment.
To get started with moderating, editing, and deleting comments, please visit the Comments screen in the dashboard.
Commenter avatars come from Gravatar.